
Linux network tuning and consumer VPN apps solve different problems. `hystart` lives in the operating system. KloxVPN gives you WireGuard, OpenVPN, OpenConnect, and Shadowsocks in one app on five devices. If someone told you to "turn on hystart in the VPN," they mixed up two separate tools.
Before you change anything on a router or laptop, know what you are editing. `Hystart` affects how the host OS handles traffic. A VPN encrypts traffic after you connect in the app. The two can coexist on one machine, but they are not the same switch.
This guide is written for normal users who bumped into `hystart` while troubleshooting, and for admins who want a quick plain-English summary. We keep the product facts simple: $2.83/month on the yearly plan, 7-day money-back on your first purchase, and no hidden modes named after kernel variables.
You may have seen `hystart` in a forum thread, a support ticket, or a kernel log. It sounds technical, and it is — but it is not a setting inside the KloxVPN app. This page explains what `Hystart` means on Linux, and what to do if you just want a safer connection on library Wi-Fi.
Looking for a reliable VPN?
KloxVPN — from $2.83/month. Apps for every device.
What `hystart` is (in plain English)
On Linux, `hystart` is exposed under `/proc/sys/` as part of the kernel's network stack. You change it with `sysctl`, config files, or network management tools — not from KloxVPN Connect.
Consumer VPN apps exist so you do not have to touch kernel interfaces on a laptop you use for email and travel. Keep that separation in mind whenever forums mix `hystart` with app screenshots.
IPv6 and multicast tuning matter on servers and some corporate laptops. They rarely matter on a phone that only needs a stable WireGuard handshake at library Wi-Fi.
Enterprise buyers sometimes ask about sysctls on VPN appliances. That conversation belongs in infrastructure design, not in the mobile app FAQ.
Seeing `hystart` in a log does not mean your VPN is broken. It often means a monitoring tool, a distro hardening guide, or a troubleshooting paste mentioned a kernel knob unrelated to your tunnel.
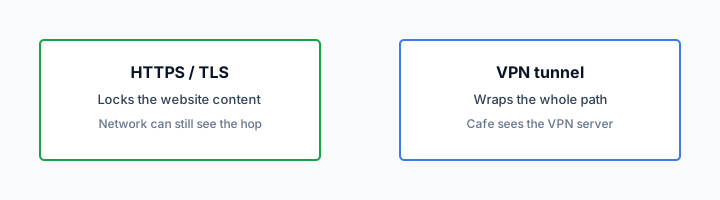
- 1Skim the diagram above.
- 2Do the numbered steps once on your real network.
- 3Use the FAQ if a sentence was too long.
- 4Follow one related article — not ten tabs.
How to read this page
| Tool | Exits slow start early using delay | Grows cwnd from a small start | Hides site IPs from cafe | Who holds the old |
|---|---|---|---|---|
| Clear HTTP, HyStart on, no VPN | Yes, if the stack ran HyStart | Yes. New TCP still starts at IW | No | Cafe, ISP, path, plus the TCP stack |
| HTTPS, HyStart on, no VPN | Yes, after the socket exists | Yes | No | Kernel plus the app plus the site |
| HTTPS, slow start only, HyStart off, no VPN | No. Doubling until ssthresh or loss | Yes | No | The stack's cwnd, no early-exit old |
| HTTPS, CUBIC after HyStart exit, no VPN | HyStart already left. CUBIC is later | Slow start still ran first | No. Cafe still sees an IP | Kernel plus the site, two leftovers after the exit |
| VPN, tunnel DNS (Klox) | No. Inner HyStart is still the TCP stack's job | No. Inner slow start is still the TCP stack's job | Yes, as a blob to the node | The VPN hop, not the ISP as a list |
| HyStart plus VPN | Inner TCP may still exit early, and RTT noise may trip it | Inner TCP may still ramp | Blob to the VPN | Kernel plus app plus the VPN hop |
| Cookie on klox.app | Unrelated | Unrelated | Unrelated | See /cookie; neither is an early exit |
HyStart exits slow start earlier using delay. Slow start grows the congestion window from a small start. CUBIC is later congestion. A VPN moves the hop. You can want the truck. Klox is not a HyStart product.
— KloxVPN consumer notes
Cloudflare Learning: What is a VPN?
Wikipedia: Virtual private network
Who actually needs to care
Server owners, homelab admins, and network engineers tune `hystart` for throughput, IPv6 behavior, or security baselines. Travelers on library Wi-Fi need a connected VPN, a finished captive portal if there is one, and maybe a protocol switch — not a sysctl lecture.
When in doubt, connect the VPN first on a network you trust, then reproduce the issue on guest Wi‑Fi. Isolate variables instead of changing ten settings at once.
What it does not do
`hystart` does not replace WireGuard, OpenVPN, OpenConnect, and Shadowsocks. It does not add devices to your plan, change your bill, or create a new Klox SKU. Privacy on an untrusted network still starts at Download: install, connect, then browse.
Bookmark DNS leak testing and kill switch behavior — those tools matter more day to day than `hystart`.
What a VPN does instead
Klox ships WireGuard, OpenVPN, OpenConnect, and Shadowsocks. WireGuard is the default when UDP works; OpenVPN is the fallback when a restrictive network blocks UDP. That choice happens in the app — not by editing `hystart`.
When in doubt, connect the VPN first on a network you trust, then reproduce the issue on guest Wi‑Fi. Isolate variables instead of changing ten settings at once.
If a friend sent you this link, ask what problem they are solving. Speed on library Wi-Fi? Use Klox. Multicast tuning on a router? That is admin work.
A VPN builds an encrypted tunnel from your device to a server you choose. Your ISP or the café router sees encrypted data going to that server — not the full list of sites you open inside the tunnel. Cloudflare's VPN overview and Wikipedia's VPN article describe that job clearly.
DNS can ride inside the tunnel so your queries do not leak to the local router. That is a VPN DNS setting, separate from kernel multicast or forwarding knobs like `hystart`.
Easy mental model
Think of `hystart` as how the engine is tuned. Think of the VPN as which road your packets take. Commuters need the road; mechanics tune the engine.
Linux documentation is written for operators. This article translates one knob into consumer language so you can close the tab and move on.
Product limits stay the same
Klox allows five devices on one subscription, $2.83/month on the yearly plan, with 7-day money-back on your first purchase. None of that changes because a kernel variable exists.
Write down what you changed when you tune sysctls. Future you — and your teammates — will need the paper trail.
What to do on your phone or laptop
If your goal is privacy on library Wi-Fi, start with the Klox app: join Wi‑Fi, finish any sign-in page, then tap Connect. Use WireGuard first. If the handshake never completes, switch once to OpenVPN.
Linux documentation is written for operators. This article translates one knob into consumer language so you can close the tab and move on.
Consumer VPN apps exist so you do not have to touch kernel interfaces on a laptop you use for email and travel. Keep that separation in mind whenever forums mix `hystart` with app screenshots.
When in doubt, connect the VPN first on a network you trust, then reproduce the issue on guest Wi‑Fi. Isolate variables instead of changing ten settings at once.
Run a leak test after you connect — not while you are still on a login screen. DNS leak basics and kill switch behavior are the right follow-ups if results look wrong.

When support asks for logs
Send app version, OS version, and which protocol worked (WireGuard, OpenVPN, OpenConnect, or Shadowsocks) on another network. Mention `hystart` only if you manage the machine and changed it on purpose.
Enterprise buyers sometimes ask about sysctls on VPN appliances. That conversation belongs in infrastructure design, not in the mobile app FAQ.
When to stop troubleshooting here
If the tunnel connects and DNS looks correct, `hystart` is probably a distraction. Close this tab and go back to work.
If a friend sent you this link, ask what problem they are solving. Speed on library Wi-Fi? Use Klox. Multicast tuning on a router? That is admin work.
If you administer a Linux server
Document why you changed `hystart` and roll back if routing or IPv6 breaks. A bad sysctl edit can drop packets silently; a VPN misconfiguration usually fails loudly at connect time.
Sysadmins sometimes tune `hystart` on VPN servers or gateways for performance and security. That work happens in Ansible, systemd, or `/etc/sysctl.d/` — not in end-user consumer apps.
Write down what you changed when you tune sysctls. Future you — and your teammates — will need the paper trail.
Consumer Klox apps never required `hystart` changes on your laptop for normal use. Treat any guide that says otherwise as mislabeled.
Enterprise buyers sometimes ask about sysctls on VPN appliances. That conversation belongs in infrastructure design, not in the mobile app FAQ.
Testing safely
Change one variable at a time on lab hardware. Compare `sysctl hystart` before and after. Keep backups of configs.
Bookmark DNS leak testing and kill switch behavior — those tools matter more day to day than `hystart`.
Separate tickets
If a user says "VPN broken" and attaches `hystart` output, split the issue: tunnel team for Connect, platform team for kernel tuning.
When in doubt, connect the VPN first on a network you trust, then reproduce the issue on guest Wi‑Fi. Isolate variables instead of changing ten settings at once.
Common mistakes
Enterprise buyers sometimes ask about sysctls on VPN appliances. That conversation belongs in infrastructure design, not in the mobile app FAQ.
Mistake 2: Assuming HTTPS on a website replaces a VPN. TLS protects the page content; the network may still see where you connect unless you tunnel.
Mistake 3: Connecting the VPN before a captive portal finishes. The sign-in page never loads and it looks like the VPN failed.
Klox publishes honest limits: five devices, $2.83/month on the yearly plan, 7-day money-back on your first purchase. No hidden `hystart` mode will appear in a future update because it was never part of the product.
Write down what you changed when you tune sysctls. Future you — and your teammates — will need the paper trail.
Better habits
Portal → Connect → test. Keep WireGuard as default. Switch protocol once. Use pricing if you need a plan refresher.
Consumer VPN apps exist so you do not have to touch kernel interfaces on a laptop you use for email and travel. Keep that separation in mind whenever forums mix `hystart` with app screenshots.
White-label partners
If you rebrand Klox, `hystart` still is not a partner-facing feature toggle. Branding changes the app skin; the tunnel stays WireGuard, OpenVPN, OpenConnect, and Shadowsocks.
Klox publishes honest limits: five devices, $2.83/month on the yearly plan, 7-day money-back on your first purchase. No hidden `hystart` mode will appear in a future update because it was never part of the product.
Troubleshooting without touching `hystart`
Start with basics: can you browse without VPN on a network you trust? If yes, the issue is likely the guest network or portal — not `hystart`.
Consumer VPN apps exist so you do not have to touch kernel interfaces on a laptop you use for email and travel. Keep that separation in mind whenever forums mix `hystart` with app screenshots.
Escalate to support with screenshots of the Connect screen, not dumps of unrelated sysctls.
Enterprise buyers sometimes ask about sysctls on VPN appliances. That conversation belongs in infrastructure design, not in the mobile app FAQ.
Reboot the device if the network profile is stuck. Windows and macOS sometimes cache bad routes after a failed VPN attempt.
Leak tests
After a successful connect, run a DNS leak check. If leaks appear, fix DNS settings inside the app before editing Linux knobs.
When in doubt, connect the VPN first on a network you trust, then reproduce the issue on guest Wi‑Fi. Isolate variables instead of changing ten settings at once.
Kill switch
If traffic stops entirely, temporarily disable the kill switch to finish a captive portal, then turn it back on.
Bookmark DNS leak testing and kill switch behavior — those tools matter more day to day than `hystart`.
Glossary in one minute
VPN tunnel: encrypted link between your device and a VPN server; configured in the Klox app.
Enterprise buyers sometimes ask about sysctls on VPN appliances. That conversation belongs in infrastructure design, not in the mobile app FAQ.
Captive portal: the hotel or café login page that must complete before full internet access.
When in doubt, connect the VPN first on a network you trust, then reproduce the issue on guest Wi‑Fi. Isolate variables instead of changing ten settings at once.
WireGuard, OpenVPN, OpenConnect, Shadowsocks: the four protocols Klox ships (WireGuard, OpenVPN, OpenConnect, Shadowsocks). Pick in app settings, not via sysctls.
Further reading
What is a VPN? · WireGuard vs OpenVPN · DNS leak guide
Linux documentation is written for operators. This article translates one knob into consumer language so you can close the tab and move on.
For admins
Keep `hystart` changes in infrastructure repos with change tickets. Consumer support should rarely mention it.
Write down what you changed when you tune sysctls. Future you — and your teammates — will need the paper trail.
FAQ-style scenarios
Scenario: A blog told me to set `hystart` to fix VPN speed. Answer: Tune servers you control if you know how; consumers should pick a closer VPN server or switch protocol.
Scenario: I just want privacy at library Wi-Fi. Answer: Portal → Connect → done. Ignore `hystart` unless you admin the gateway.
Scenario: IPv6 behaves oddly on my network. Answer: IPv6 issues may involve router settings and VPN config. Fix one layer at a time.
When in doubt, connect the VPN first on a network you trust, then reproduce the issue on guest Wi‑Fi. Isolate variables instead of changing ten settings at once.
Scenario: I found `hystart` in Android settings. Answer: Phone OS internals differ; you still connect via the Klox app, not sysctl.
Still stuck?
Contact support with app version and OS. Leave `hystart` out unless you changed it yourself.
Enterprise buyers sometimes ask about sysctls on VPN appliances. That conversation belongs in infrastructure design, not in the mobile app FAQ.
Pricing reminder
$2.83/month on the yearly plan. five devices. 7-day money-back on your first purchase.
If a friend sent you this link, ask what problem they are solving. Speed on library Wi-Fi? Use Klox. Multicast tuning on a router? That is admin work.
Key Takeaways
Key takeaway: `hystart` is an OS-level control; KloxVPN is the app-level tunnel (WireGuard, OpenVPN, OpenConnect, and Shadowsocks, five devices, $2.83/month on the yearly plan, 7-day money-back on your first purchase).
Download · Pricing · Linux ip-sysctl docs
If you admin Linux, tune `hystart` carefully and document changes. If you travel, portal first, connect second, test once.
Related Resources
Need a VPN, not a sysctl?
KloxVPN — WireGuard, OpenVPN, OpenConnect, and Shadowsocks, five devices, $2.83/month on the yearly plan. 7-day money-back on your first purchase.
See pricingFrequently Asked Questions
KloxVPN Team
Experts in VPN infrastructure, network security, and online privacy. The KloxVPN team has been building and operating VPN services since 2019, providing consumer and white-label VPN solutions to thousands of users worldwide.